New to Rust? Grab our free Rust for Beginners eBook Get it free →
Hybrid Blockchain: Architecture, Use Cases, and Limits

A hybrid blockchain is an architecture that combines restricted data handling with a public verification surface. The useful question is not whether it is a third network category. It is which data, participants, and proofs need different access rules.
What is a hybrid blockchain?
In a hybrid design, approved participants handle confidential business data in a permissioned system, while an external audience can verify selected facts through a public chain or another shared proof layer. The public layer might hold a hash, a timestamp, a transaction reference, or a status change rather than the underlying record.
The phrase describes an architecture, not one protocol with fixed rules. You need to specify the two systems, the data that crosses their boundary, and who verifies each result.
How the architecture separates data from proof
A purchase order shows the separation clearly. Supplier terms, amounts, and personal details can remain in a permissioned application, while the application publishes a cryptographic commitment for that exact record.
Later, an authorized party hashes the retained record again and compares it with the commitment. A match shows that the supplied bytes have not changed since the commitment was created. It does not prove that the record was correct when someone entered it.
The smallest hash-anchor example
The following Python example uses Python’s hashlib module. It keeps the private record inside the program, publishes only a short identifier and hash prefix for display, then verifies the full commitment locally.
import hashlib

private_record = b"purchase-order=PO-4821|supplier=Northwind|amount=1250"
commitment = hashlib.sha256(private_record).hexdigest()
public_anchor = {"record_id": "PO-4821", "sha256_prefix": commitment[:16]}

print("Private record stays with approved participants")
print("Public anchor:", public_anchor)
print("Full proof matches:", hashlib.sha256(private_record).hexdigest() == commitment)
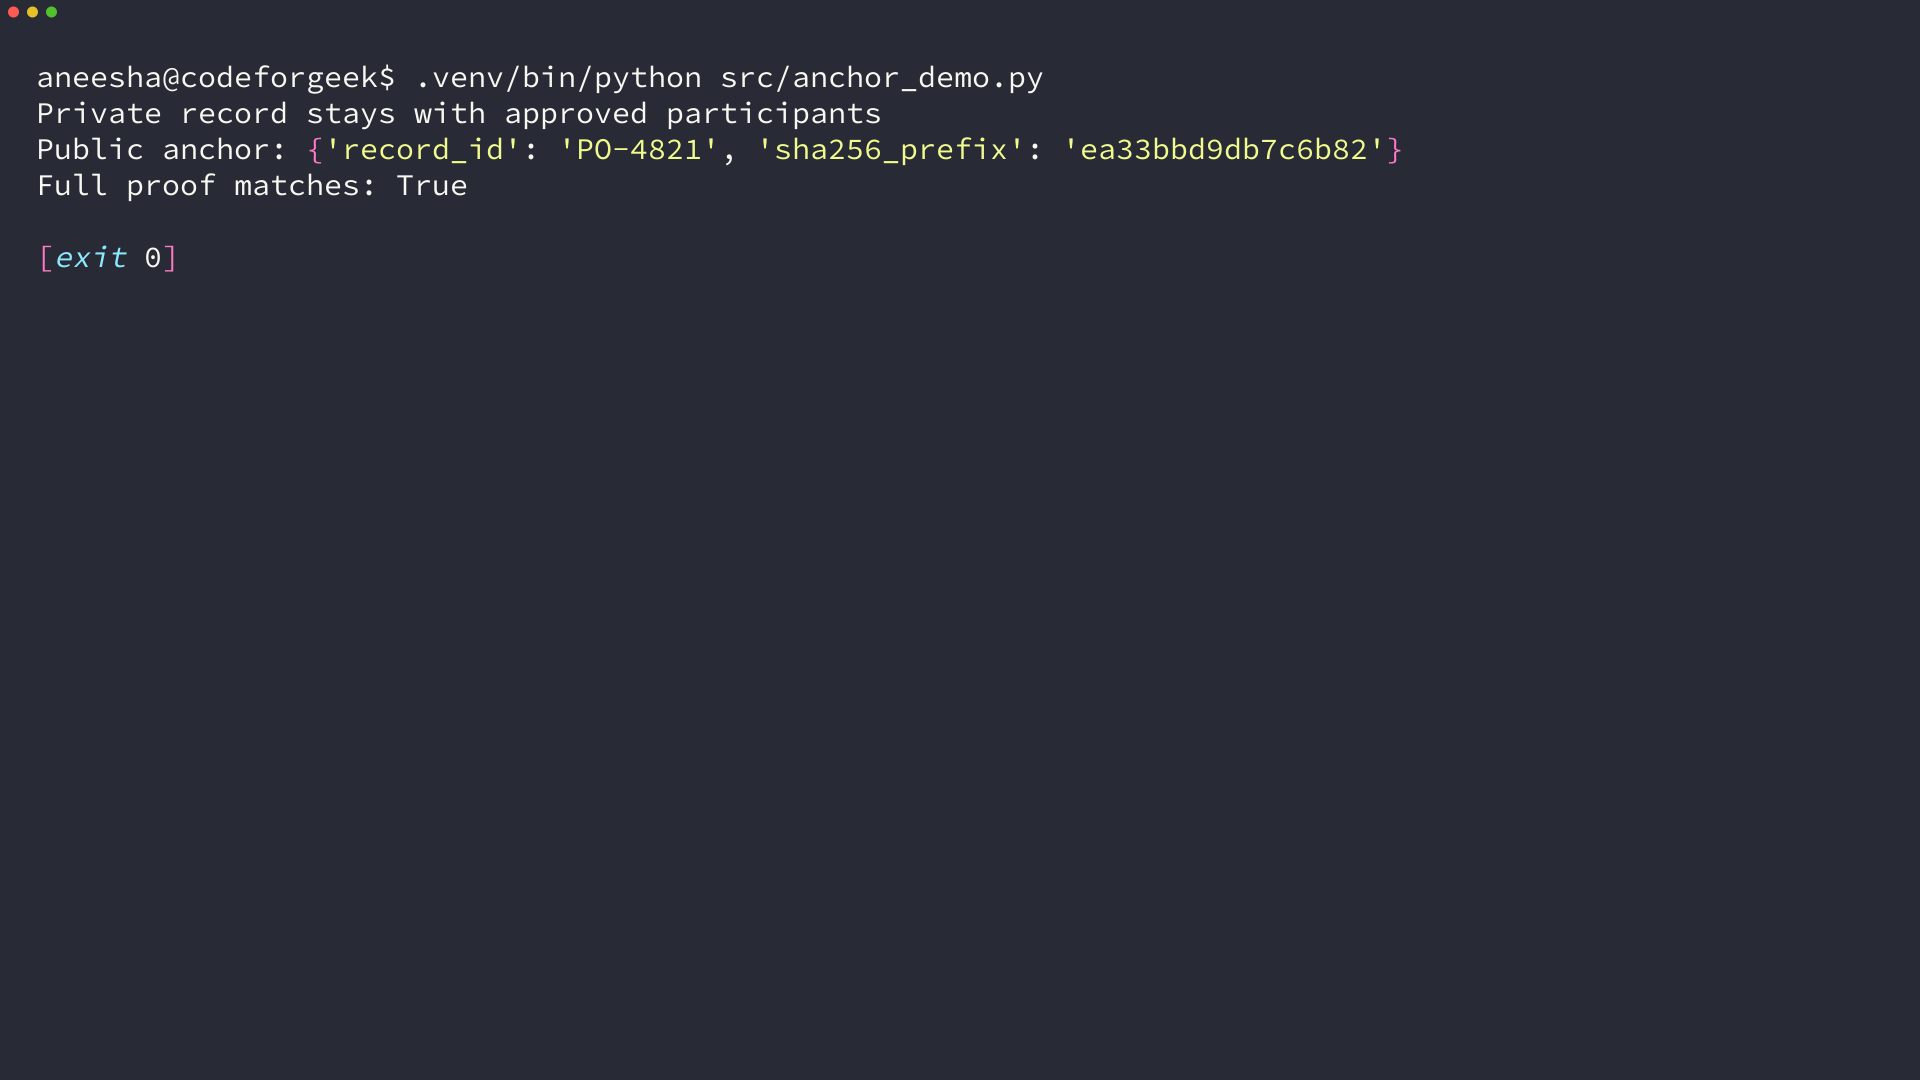
The displayed prefix is only a convenient label. A verifier must compare the complete SHA-256 value, use an agreed record format, and protect the original record. A hash does not hide a predictable low-entropy value from someone who can guess and hash candidates.
Public, private, consortium, and hybrid designs solve different access problems
Network labels matter less than the operating constraints. Start with participant identity, data visibility, validation authority, and whether an outside party must independently check an event.
| Design | Who participates | What you trade |
|---|---|---|
| Public blockchain | Anyone who meets the network rules | Broad verifiability, with limited confidentiality |
| Private or permissioned blockchain | Known members approved by an operator | Access control, with less independent public verification |
| Consortium blockchain | Several organizations under shared governance | Joint control, with more coordination overhead |
| Hybrid architecture | Private participants plus an external verification surface | Selective disclosure, with a harder integration and governance job |
Hyperledger Fabric illustrates the permissioned side of this decision. Its private data collections send sensitive data only to authorized organizations, while a hash of that data is written to the channel ledger so peers can validate a transaction without receiving the private value.
When a hybrid design is a good fit
Use this approach when parties need confidentiality for the business record but an auditor, regulator, customer, or partner needs evidence that a disclosed record has not been altered. Supply-chain attestations, document provenance, and cross-company workflows can fit that boundary.
A hybrid design is not an automatic security upgrade. Your organization still needs identity controls, key rotation, retention rules, dispute handling, backup and recovery, and a definition of which system settles a conflict.
Choose the boundary before choosing a platform
Write down the record that must remain confidential, the event that needs outside verification, and the party allowed to publish the proof. Then define how a verifier obtains the original record, computes the commitment, and responds when the proof does not match.
If every participant is already trusted and no independent verification is required, a permissioned database or ledger may be simpler. If every record must be publicly inspectable, adding a private layer can create cost without improving the reader’s task.
Frequently asked questions
These boundaries prevent a hash anchor from being mistaken for a complete confidentiality or trust system.
Is a hybrid blockchain a separate blockchain type?
Hybrid blockchain usually describes an architecture that combines restricted data handling with a public or shared verification layer. The protocol, governance, and data boundary vary by implementation.
Does storing a hash on a public blockchain keep data private?
A hash can avoid publishing the source record, but it is not encryption. Predictable or low-entropy values can be guessed and hashed, so sensitive records still need access controls and a careful commitment design.
What does a hash anchor prove?
It can show that a supplied record produces the same commitment as the stored value. It does not prove that the record was accurate when it was created or identify who entered it.
Sources to inspect
Hyperledger Fabric’s private data documentation explains how authorized peers receive private data while hashes reach the channel ledger. Avalanche’s L1 documentation is useful when you need to evaluate a dedicated network with its own validator set and rules.
Start your design review with one record and one verifier. If you cannot state the exact proof and the party that checks it, you have not defined the hybrid boundary yet.